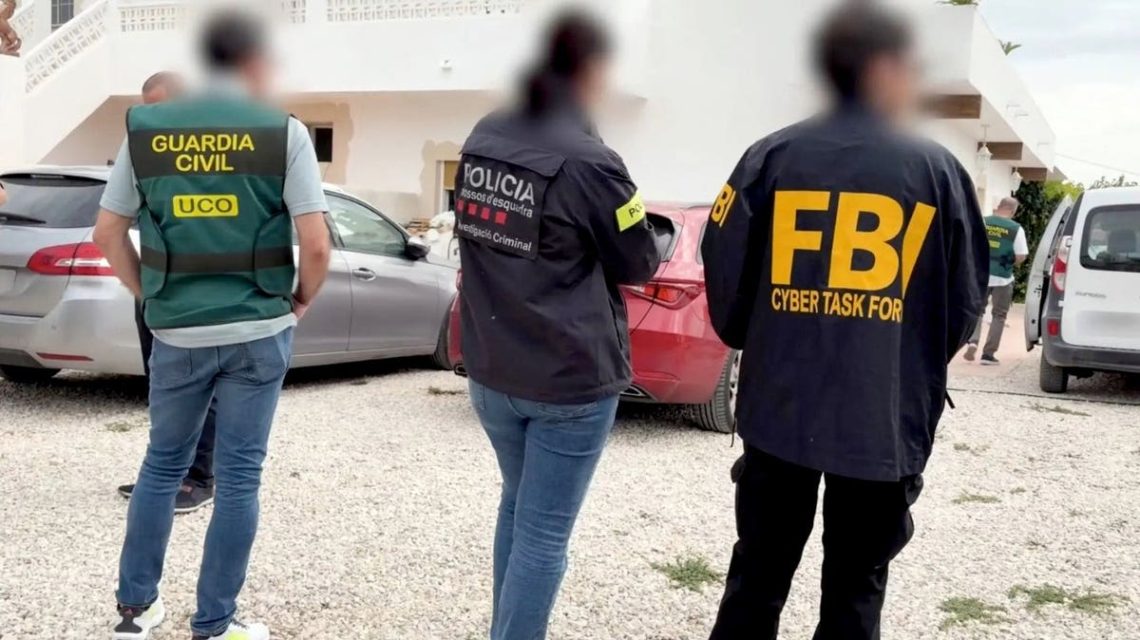
Investigators recently identified a surprising suspect in an international ransomware operation: a 16-year-old mastermind. This revelation underlines the ease of access to cybercrime. The teenager allegedly led KillSec, a cybercrime group responsible for approximately 1,000 attacks globally, with about 500 of those deemed successful. Authorities have now halted KillSec, taking its servers offline and securing 110 terabytes of stolen data.
How KillSec Operated
KillSec’s methods illustrate how ransomware attackers exploit poorly protected systems. They leverage stolen files for ransom, demanding payment by threatening to release sensitive data. Authorities have noted that artificial intelligence plays a role in facilitating these attacks, aiding in infrastructure maintenance and victim identification.
Recent Crackdown on KillSec
A collaborative international operation, Operation KillSwitch, involving multiple countries including the United States, dismantled KillSec on September 30th. Law enforcement carried out searches in Greece, Romania, Spain, and the United Kingdom, arresting three suspects and seizing five servers.
Insights into KillSec’s Strategy
KillSec’s approach highlights the evolution of ransomware. Rather than locking files, attackers increasingly rely on the threat of publishing stolen data. Europol reports they received substantial ransoms from victims, demonstrating the effectiveness of this tactic.
Ransomware Prevention Tips
While ransomware attacks often target organizations, individuals can adopt several security measures:
- Install software and security updates regularly to fix vulnerabilities.
- Use strong, unique passwords and consider a password manager to store them.
- Enable two-factor authentication for an additional layer of security.
- Regularly back up important files, both in the cloud and offline.
- Be cautious with unexpected downloads or email attachments.
- Use reputable security software and keep it updated.
- Know how to respond if ransomware strikes your system.
Current State of the Investigation
The investigation into KillSec continues, focusing on seized evidence such as computers and cryptocurrency transactions. Although authorities disrupted the group’s operations, ransomware organizations often rebrand and reappear, emphasizing the importance of prevention.
Closing Thoughts
The arrest of a teenager allegedly involved in a significant ransomware operation highlights the accessibility of cybercrime. Familiar software vulnerabilities underscore the need for fundamental security practices. Regular updates and multifactor authentication should be standard measures for protecting devices and accounts.
For additional cybersecurity tips and insights, visit CyberGuy.com or subscribe to their newsletter. Monitor your tech habits to guard against potential threats, understanding that proactive security can avert many risks.
 Concerns Surrounding ChatGPT for Teens
 OpenAI Researchers Challenge Their Dismissals in Public Letter
 AI’s Role in Enhancing Human Connection Through Innovative Ventures
 OpenAI Reveals Russian and Iranian AI-Driven Influence Operations
 Vance Targets Microsoft’s Use of Foreign Workers
 Advanced Scam Protection Techniques for Your Devices