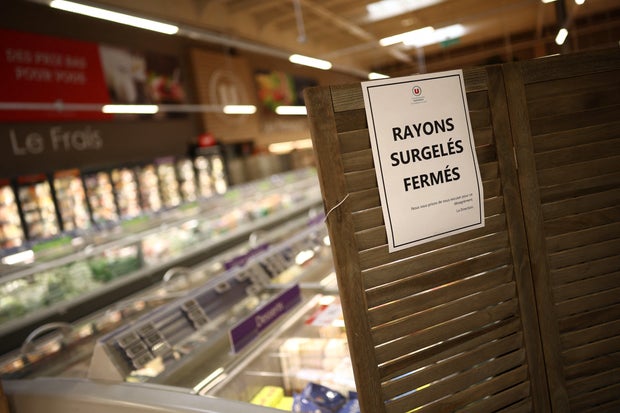
French authorities suspect Iran’s involvement in extensive cyberattacks targeting refrigeration units at grocery stores across the nation. According to the Paris prosecutor’s office, these attacks were attributed to a cyber unit affiliated with Iran’s Islamic Revolutionary Guard Corps. The coordinated hacks were executed in October, impacting major supermarket chains.
On October 11, about 700 retail locations in France were compromised, leading to a substantial loss of food and triggering approximately twenty fires. The overheating refrigeration units were the cause of these incidents. This disruption was not isolated to France, as similar cyberattacks also affected supermarkets in Belgium, Luxembourg, and Sweden in the subsequent weeks.
Moreover, a separate cyberattack targeted blood banks in France, although no damage was inflicted on the stored products and samples. In the United States, the Department of the Army Criminal Investigation Division is probing refrigeration outages at six military bases since August, according to Thomas Hamilton, a public affairs officer for the department.
No official connections have been made between these incidents in France, the U.S., and other affected European countries. However, the Paris public prosecutor’s office launched a judicial investigation into charges, such as fraudulent interference with automated data systems and causing hazardous damage.
The alleged offenses are seen as further aggravated because they were intended to benefit a foreign power, namely Iran. The investigation focuses on the leader of an Iranian group known as “Shahid Kaveh.” This group is reportedly linked to the IRGC’s Electronic and Cyber Center (IRGC-ECC), along with his deputies and other potential accomplices.
It was revealed that the attackers manipulated web interfaces to remotely control refrigeration equipment. They triggered indefinite defrost cycles while disabling essential safety alerts that would indicate temperature anomalies. The investigation uncovered methodologies typical of this Iranian unit, including using the Persian language and Iranian IP addresses.
The attackers gained remote control of the equipment via web interfaces, initiating indefinite, abnormal defrost cycles while simultaneously disabling safety alerts.
The FBI’s cybercrime branch recently noted global malicious cyber activities targeting industrial refrigeration and monitoring systems. They warned that vulnerabilities in unpatched or internet-accessible controllers could allow unwanted alterations, leading to significant inventory and equipment losses. The FBI advises organizations to disconnect these systems from the public internet and protect them with firewalls.
No immediate response came from Iranian authorities regarding the French allegations. The Iranian regime has previously threatened to escalate its retaliation related to conflicts with the U.S., utilizing unspecified asymmetrical methods.
Karine Barzegar of CBS News contributed to this report.
 G7 Foreign Ministers Discuss Global Crises Amid U.S. Political Changes
 Feud and Legal Battle in New York Family Dynasty
 Political Shifts and Concerns Post-Midterms
 Death Toll Rises After Krakow Shooting
 Villa Vie Odyssey Faces Legal Challenges After Halting Operations
 Trump Shares AI-Generated Video Featuring UFC Personalities